AI and the PHP Security Crisis: What Developers Should Know
Critical PHP runtime vulnerabilities put AI-assisted security research in the spotlight. Here is what happened, what AI contributed, and what software teams should do next.
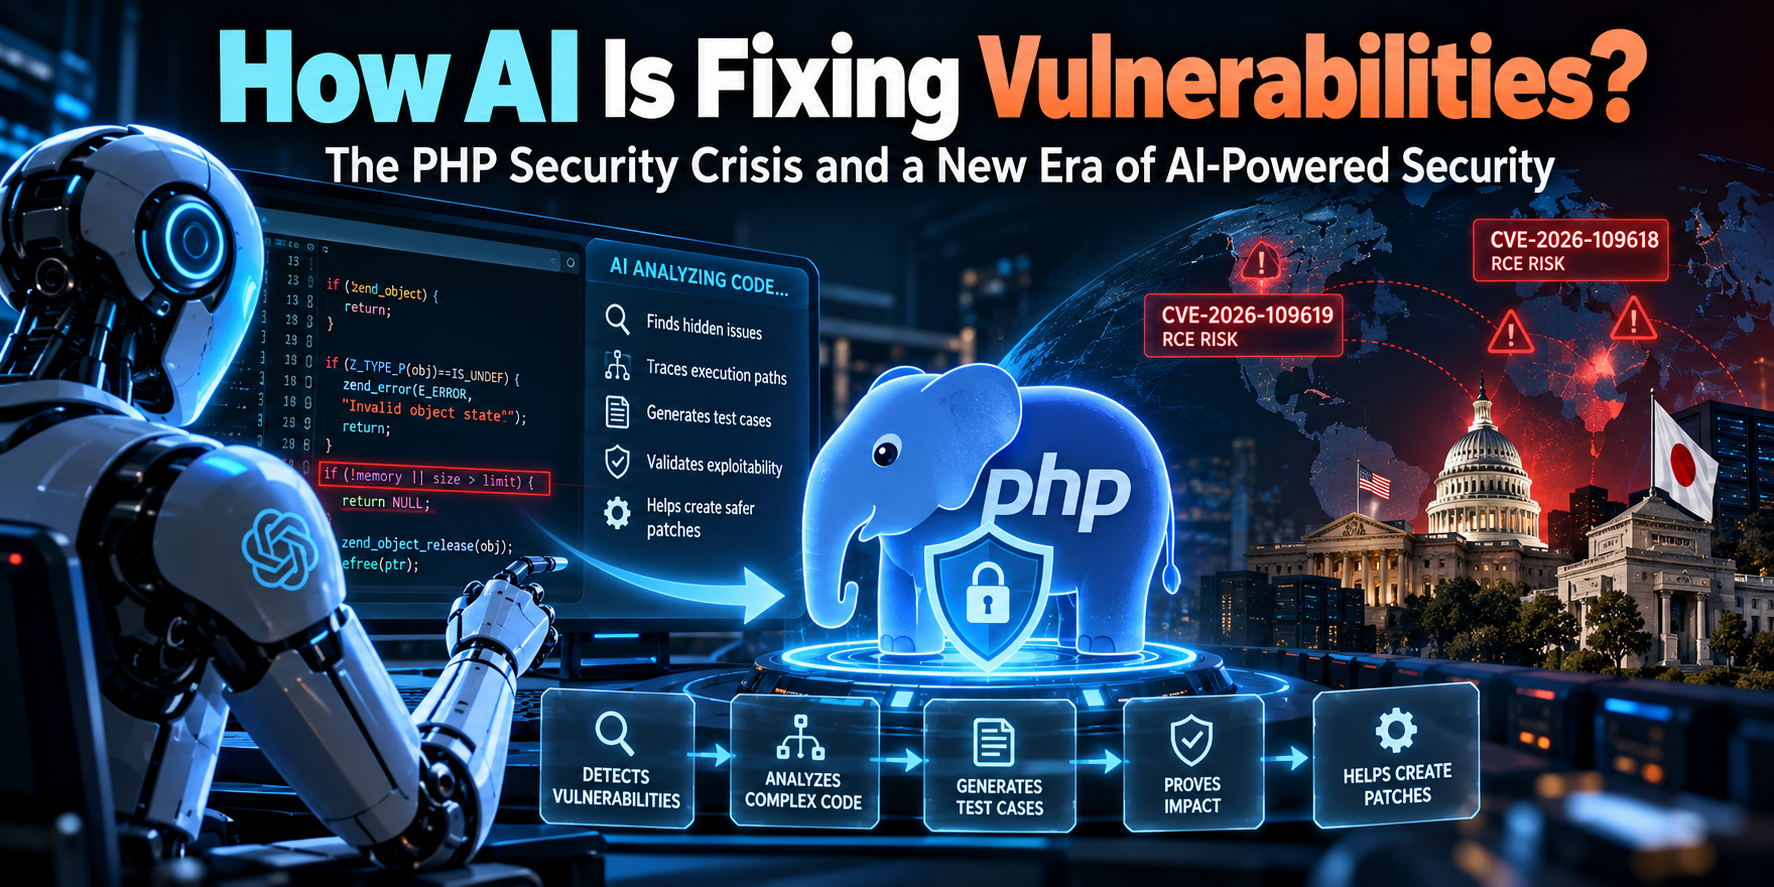
In October 2026, emergency security updates for PHP brought a difficult question into focus: what happens when researchers can use AI to investigate deep software vulnerabilities faster, while the rest of the industry still needs time to verify findings and patch every affected system?
The PHP project disclosed two critical runtime vulnerabilities, CVE-2026-109618 and CVE-2026-109619. Both were rated 9.2 out of 10 under CVSS 4.0. The U.S. National Security Agency advised organizations to update affected installations promptly or take vulnerable systems offline if they could not patch them.
Official fixed versions included PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Always check the official PHP security advisory and your operating-system, hosting or container provider's instructions for the release that applies to your deployment.
The story is not simply that AI found a bug. It is about how a concern becomes credible evidence, how maintainers coordinate a fix, and how organizations make sure that fix reaches production.
The warning signs existed before the headlines
According to the PHP Foundation's account of the incident, initial signs of an underlying issue had been identified in 2024. At the time, a convincing, practical attack path had not been established, and other security work competed for attention.
That gap matters. A suspicious memory operation or unusual error path may deserve investigation, but identifying a possible flaw is not the same as proving what an attacker could do with it. Teams need reproducible evidence to assess severity, prioritize work and decide whether a change is safe to ship.
The PHP Foundation described the delay as a structural failure. The useful lesson is not to blame individuals for missing a signal; it is to improve the process that evaluates reports, funds maintenance and gets validated fixes into releases.
How AI-assisted research changed the investigation
During 2026, researchers used AI-assisted analysis alongside conventional security research. The PHP Foundation said its earlier security work included Anthropic's Claude Mythos. Later work involved additional tools and partners: Calif identified a critical flaw with the same root cause as the issue first noticed in 2024, and OpenAI independently reported the same root cause on August 11. Further attack paths were reported in the weeks that followed.
OpenAI's Patch the Planet research, Calif's security audit, and independent findings from Wiz contributed to identifying and validating attack paths. These efforts helped demonstrate practical impact and move remediation forward.
AI can help researchers navigate large codebases, trace complex execution paths, form hypotheses about failure conditions and suggest candidate tests. Those capabilities can help turn an abstract concern into evidence that maintainers can assess.
Important distinction: AI did not independently repair PHP. Researchers investigated and reported findings, PHP maintainers reviewed the evidence and developed fixes, and release teams coordinated security updates.
Why these PHP runtime flaws were serious
PHP must manage memory, errors and internal objects while processing application requests. The vulnerabilities involved unsafe behavior in the runtime itself—not simply mistakes in an individual website's business logic.
Out-of-memory error handling
CVE-2026-109618 involved handling an out-of-memory condition: a program could not obtain the memory it needed to continue normally. In simplified terms, if an operation fails while internal request data is only partly initialized, later cleanup code may incorrectly assume that the data is complete and valid. Error-handling paths need the same scrutiny as the expected, successful path.
Stale state and memory lifetime
CVE-2026-109619 involved request-owned internal state outliving the memory it depended on. This is the class of issue known as use-after-free: software accesses memory after it has been released, when that memory may already have been reused for something else.
The technical conditions are specific to the affected runtime and deployment. Researchers demonstrated that the flaws could enable remote code execution, which is why organizations were urged to take the updates seriously. For technical context, see Google Cloud's analysis.
What AI can—and cannot—do in vulnerability research
AI-assisted security research is a set of tools used at different stages, not a magic button that turns a codebase into a secure one.
- Code analysis: identify suspicious assumptions around memory, input validation or error handling.
- Hypothesis generation: suggest edge cases and execution paths that researchers can investigate.
- Test development: help create candidate tests to check whether a behavior is repeatable.
- Impact assessment: support investigation into whether an issue is more than a crash or harmless anomaly.
- Patch review: compare a fix with the original code and suggest regression tests or related areas to inspect.
A model can also produce a plausible but incorrect explanation. A crash alone does not prove remote code execution, and generated tests are not a substitute for careful review. Findings become actionable when qualified researchers can reproduce them, explain their impact and share evidence maintainers can verify.
The wider lesson for software security
Node.js also published security updates on October 21, addressing separate high-severity issues involving areas such as Brotli decompression, DNS resolution and TLS hostname validation. Their timing does not prove that AI found every issue or that the PHP and Node.js vulnerabilities shared a cause. Together, however, the updates are a reminder that widely deployed runtimes need ongoing security work.
Faster discovery can help defenders, but it can also shorten the time attackers need to study a public fix. After a patch is released, attackers may compare updated and vulnerable code—a technique called patch diffing—and look for systems that have not yet been updated. That makes coordinated disclosure and rapid deployment important parts of the same response.
What PHP developers and operators should do
- Check exposure. Identify the PHP versions running across servers, containers, staging environments and production.
- Use authoritative upgrade guidance. Consult the official PHP advisory and instructions from your hosting, operating-system or container provider.
- Install an applicable patched release. Plan and test the upgrade using your normal change-management process; do not assume an application-level workaround replaces a runtime update.
- Verify deployment. Confirm the updated runtime is actually serving requests, including after restarting or redeploying services where required.
- Keep dependencies and runtimes current. Make patching routine rather than waiting for an emergency headline.
Security teams and engineering leaders should also make room for maintenance work, reproducible testing and responsible vulnerability reporting. These are core parts of building software, not tasks to postpone until after a crisis.
Frequently asked questions
What were the 2026 PHP vulnerabilities?
CVE-2026-109618 and CVE-2026-109619 were critical vulnerabilities in the PHP runtime. Consult the official PHP advisory for affected releases and the recommended updates.
Did AI independently discover and fix the PHP vulnerabilities?
No. AI-assisted analysis supported parts of the research, but people investigated and validated findings, and PHP maintainers reviewed and shipped fixes.
What should a team do if it cannot patch immediately?
Follow the current official advisory and guidance from your hosting or infrastructure provider. The NSA advised taking affected systems offline if they could not be patched; organizations should assess their exposure and response with their security and operations teams.
Can AI guarantee that software is secure?
No. AI can help find and investigate potential issues, but it can miss real defects or produce false positives. Human review, testing, coordinated disclosure and timely patching remain essential.
Final takeaway
The PHP security incident shows how AI-assisted research can help investigators explore complicated code and build evidence around a suspected vulnerability. It also shows that discovery is only one part of security: teams still need maintainers, validated fixes, coordinated releases and organizations that deploy updates promptly.
AI may help us find problems faster. The real test is whether we can verify, fix and patch them before attackers take advantage.